What Is the Software Development Life Cycle (SDLC) in 2026?

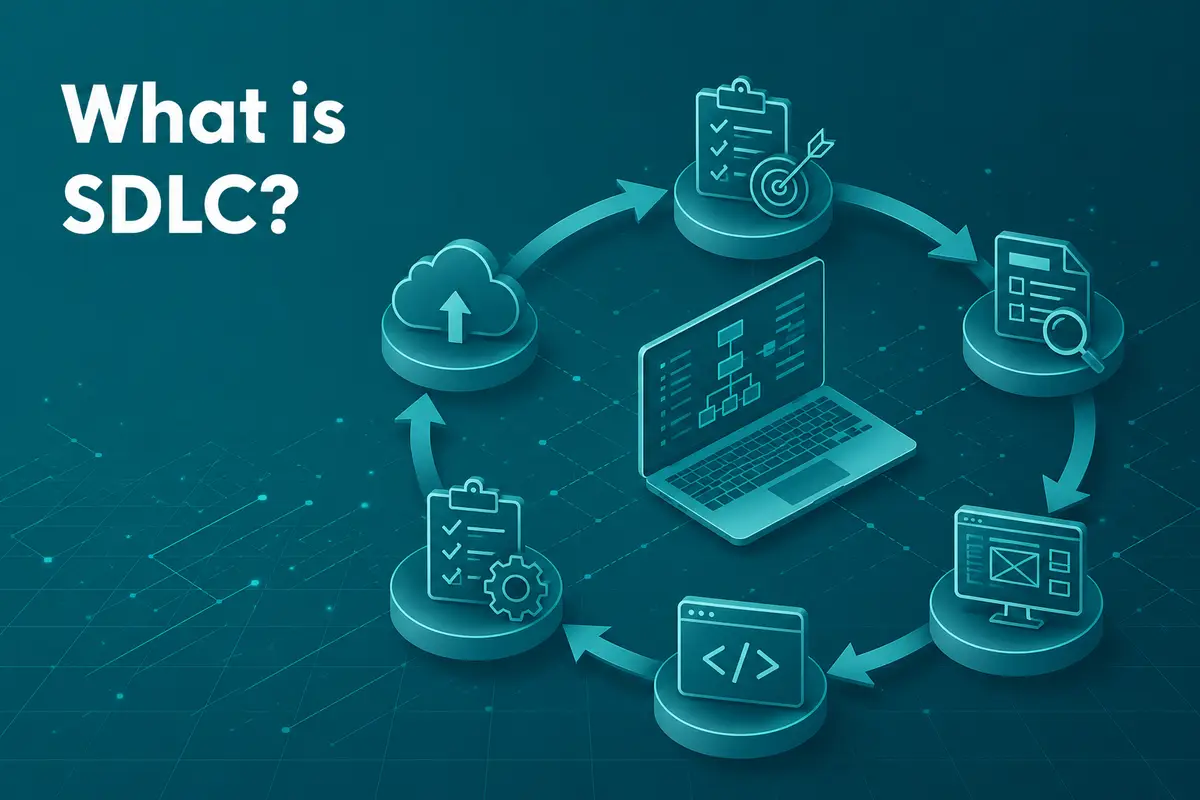
A missed requirement rarely stays small. By the time it surfaces in testing, or worse, once the software is already live, fixing it can cost far more than catching it on day one.
The software development life cycle (SDLC) exists to prevent this. It gives engineering teams a repeatable structure for building software, from the first conversation about scope to the last patch after launch. Micro, small and medium-sized enterprises make up around 90% of businesses worldwide and 60 to 70% of global employment, according to the United Nations, so a working process matters well beyond enterprise giants.
Two forces are reshaping how that structure works in 2026. AI-assisted coding is changing how fast teams move through each phase. Tighter security regulations are changing what "finished" actually means before software ships. This guide walks through both, alongside the models, phases, and roles that make up a working SDLC.
What is the SDLC and how does it work?
Strip away the jargon, and the SDLC is just a structured way of planning, building, testing, releasing, and maintaining software. It sets clear entry and exit criteria for every stage. That way, a team always knows what "done" looks like before moving on.
The goal is high quality at a lower cost in the shortest workable time. Nobody hits all three perfectly, and that tension between speed, cost and quality is why a defined process exists.
The current governing standard is ISO/IEC/IEEE 12207:2026, published in April 2026 to replace the 2017 edition. It covers software life cycle processes across acquisition, supply, development, operation and maintenance, and applies in industries as different as aerospace, finance and healthcare.
Roles and responsibilities in the SDLC
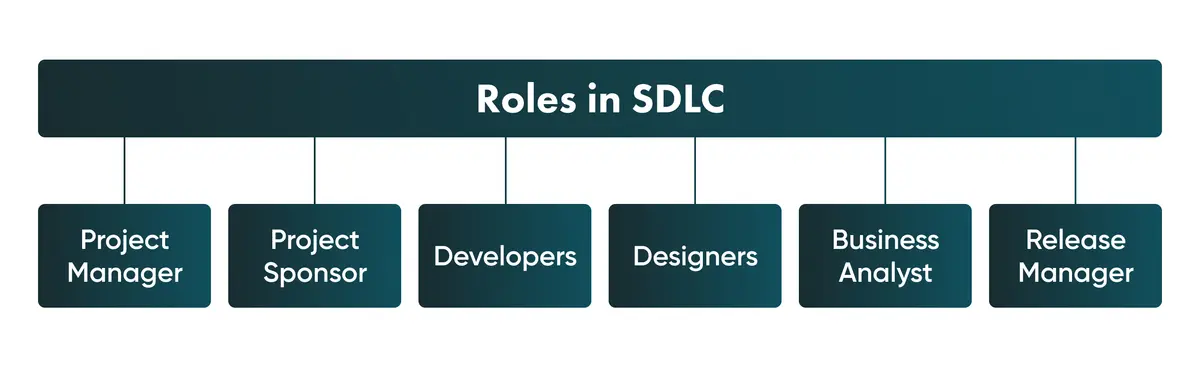
An SDLC only works if the right people make the right decisions. Here is who typically sits around the table.
Project manager
The project manager plans the work, assigns it and tracks it. They own the deadlines and the budget and are usually the first to notice when either starts slipping.
Project sponsor
The sponsor is the senior manager who backs the project: they provide resources and support and keep communication open between the project manager and other decision-makers.
Developers
Developers write, test, debug and maintain the code, using the languages and frameworks suited to the project. Their work differs depending on whether they specialise in frontend, backend or full-stack development, something worth understanding before hiring a full-stack development company for a project that spans both.
Designers
Designers work alongside developers and product managers on interface design and new features, turning requirements into something users can navigate.
Business analyst
The business analyst keeps the technical team and the business side aligned: they document the business process, analyse requirements and translate when the two sides talk past each other.
Release manager
The release manager plans the release schedule and manages release risk from the early stages of development through to the final rollout.
What are the 6 main SDLC models?
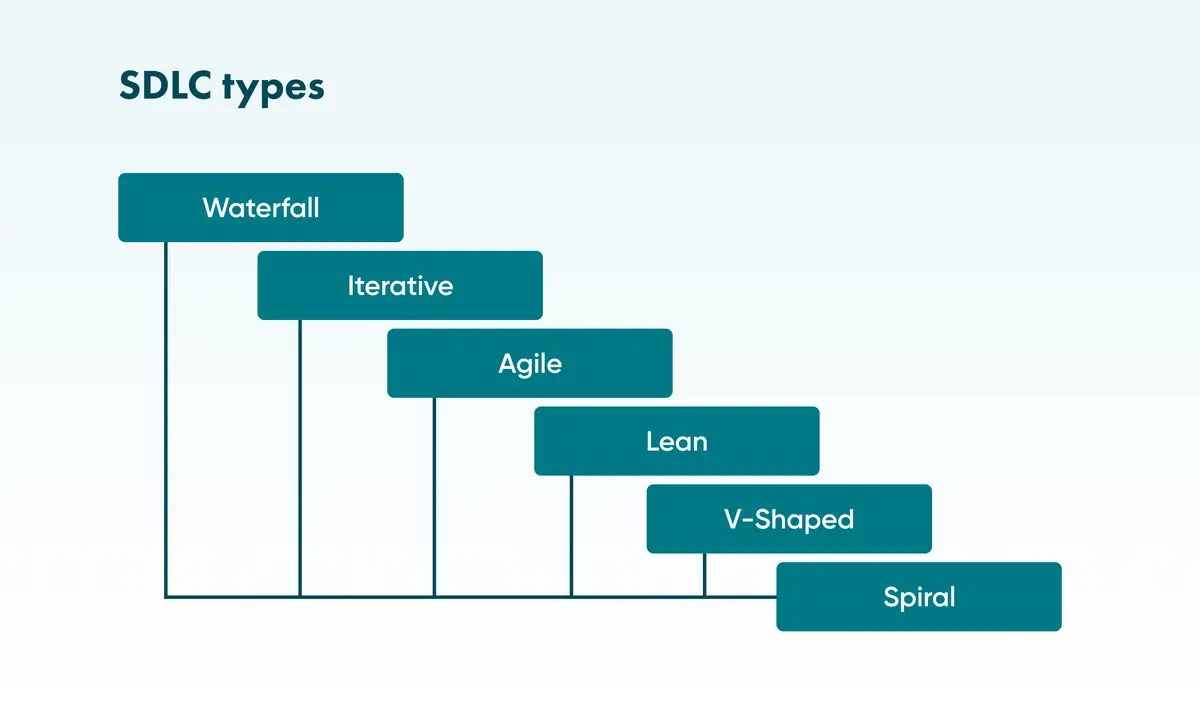
Every SDLC needs a model: a way of sequencing the phases. Here are the 6 that come up most often.
Waterfall model
Waterfall is the oldest of the six. Herbert Benington described a sequential process in 1956, and Winston W. Royce drew the now-familiar diagram in 1970, although he presented it as a risky approach and recommended iteration and feedback; the name “waterfall” came later, in 1976. The model moves through phases in strict order, each one finishing before the next begins. Fixed, well-understood requirements suit it well. Anything that needs to change mid-flight does not.
Iterative model
In the iterative model, the team delivers a working version at the end of each cycle and then repeats. It can look slower on paper, but it usually catches bugs earlier and makes changes cheaper, because nobody waits until the end to find out that something is broken.
Agile model
Agile breaks a project into builds, then breaks each build into short iterations, typically one to three weeks long. Testing happens after every iteration, and the client stays close throughout. That closeness has a cost: priorities can shift mid-project, adding work and pushing back the release.
Lean model
Lean cuts anything that does not add value for the client, whether time, money or extra functionality. Its principles include eliminating waste, deciding as late as possible and delivering as fast as possible. Teams avoid multitasking: everyone works on one task at a time.
V-shaped model
V-shaped pairs every development stage with a matching verification step, creating a disciplined process that leans hard on testing throughout. It suits projects where the requirements are clear and unlikely to shift.
Spiral model
The spiral model loops through four phases repeatedly, refining the product each time based on user feedback. It is flexible, but a project can drag on if the team keeps adding one more improvement every round. It is best suited to large, complex projects.
What are the 7 phases of the SDLC?
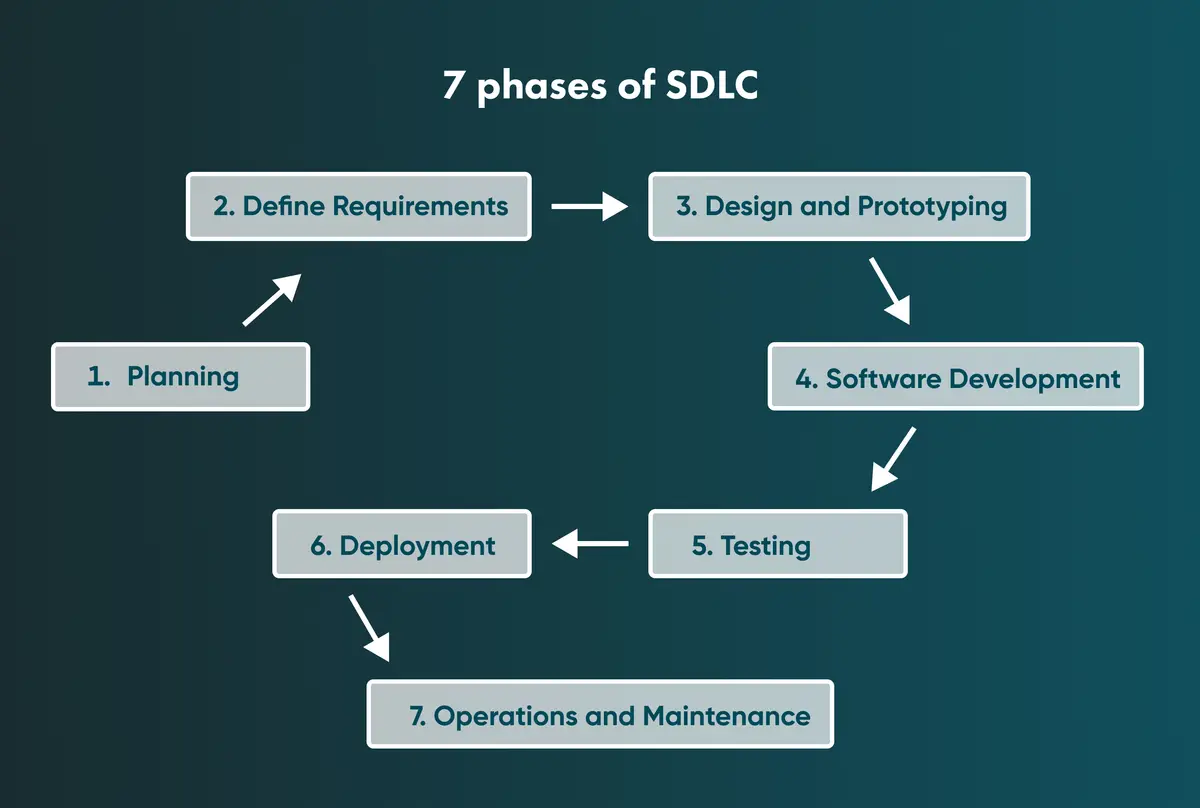
Regardless of which model a team chooses, most SDLCs move through the same 7 phases.
1. Planning or discovery
Every project needs a plan before the first line of code gets written, in the same way nobody builds a house from a mental picture alone. This phase, sometimes formally run as a discovery phase, sets goals, tools, cost estimates, and requirements. Skipping it is one of the more expensive mistakes a team can make, something we cover in more detail in our piece on the project discovery phase in software development.
2. Requirements and analysis
Here, the team gathers as much detail as possible about what the client actually needs, then documents it for later stages. Specialists set up structured communication with the client, analyse whether the proposed system can realistically meet expectations, and write it all down so nothing gets lost between meetings.
3. Design and prototyping
Developers choose the architecture, programming languages, and frameworks that fit the project. At Go Wombat, that often means Python, JavaScript, React, React Native, or Django, depending on what the product needs to do. This phase usually includes UI/UX design work and, where useful, a prototype so stakeholders can react to something concrete rather than a document. A design document then guides the rest of the team through what comes next.
4. Software development
This is where the design becomes working code. Developers build the framework in the chosen language, using compilers, debuggers, and interpreters as needed. Coordinating a team of programmers through this stage is its own discipline, one reason custom software development projects benefit from a clear process, not just skilled individuals.
5. Testing
Testing usually starts once the product reaches a dedicated environment, separate from where it was built. The goal is straightforward to state and harder to execute well: find the bugs, communicate them clearly to developers, and confirm the software meets what was agreed in the first phase. Our guide to the 7 principles of software testing and our piece on quality assurance in software engineering both go deeper into how this stage should work in practice.
6. Deployment
Deployment is when the software reaches its actual users, sometimes alongside training documentation to help them get the most out of it. Most deployment today is automated, but that does not remove every risk. Real-world use surfaces issues that no test environment quite predicts, and early user feedback often reshapes the next release.
7. Maintenance
This is the users' stage. Developers keep updating the software to match changing needs, fix bugs that only show up under real load, and close vulnerabilities as they are discovered. Ongoing IT support and maintenance are what keep this phase from becoming an afterthought.
Secure SDLC: why security can't be bolted on in 2026
Many teams still treat security as a checklist at the end of testing. That habit is becoming a legal liability as well as a technical one.
The EU Cyber Resilience Act makes security-by-design a requirement, rather than a suggestion, for digital products sold in the EU. Vulnerability and incident reporting obligations begin in September 2026, with full compliance required by December 2027, and the underlying principle, building cybersecurity in from the start rather than adding it afterwards, is exactly what a secure SDLC is meant to deliver. NIST's Secure Software Development Framework, currently being updated to version 1.2, gives teams a concrete set of tasks for embedding security into each phase rather than treating it as a separate workstream.
The cost of skipping this is not hypothetical. In 2024, a backdoor was discovered inside XZ Utils, a compression library used across most Linux distributions, after an attacker spent over two years building trust as a maintainer before quietly inserting malicious code, tracked as CVE-2024-3094 with the maximum possible severity score. It was only caught because an engineer happened to notice a small performance regression during unrelated testing. Shift-left security, the practice of testing and reviewing for vulnerabilities from the earliest phases rather than the last one, exists precisely to reduce reliance on that kind of luck.
Practically, this means threat modelling during design, automated dependency scanning during development, and a software bill of materials maintained throughout the project, not assembled after the fact. Our cybersecurity consulting and GDPR consulting work both fold into this, and we cover the broader stakes in the importance of cybersecurity for SMEs.
How AI is reshaping the SDLC in 2026
AI has moved from novelty to habit in most engineering teams. According to Stack Overflow's 2025 Developer Survey, 84% of developers use or plan to use AI tools in their workflow, up from 76% the year before, and 51% of professional developers use them daily.
AI now touches nearly every SDLC phase: requirements are drafted faster, boilerplate code is generated rather than typed, and test cases are suggested automatically. None of this replaces the phases themselves. The same survey found that developers’ trust in AI output dropped compared with the previous two years, even as daily use kept climbing.
Treat AI output the way you would treat work from a fast but occasionally careless junior developer: useful and quick, but reviewed before anything ships. Our AI services and solutions team builds this kind of review into client workflows.
SDLC benefits for SMEs
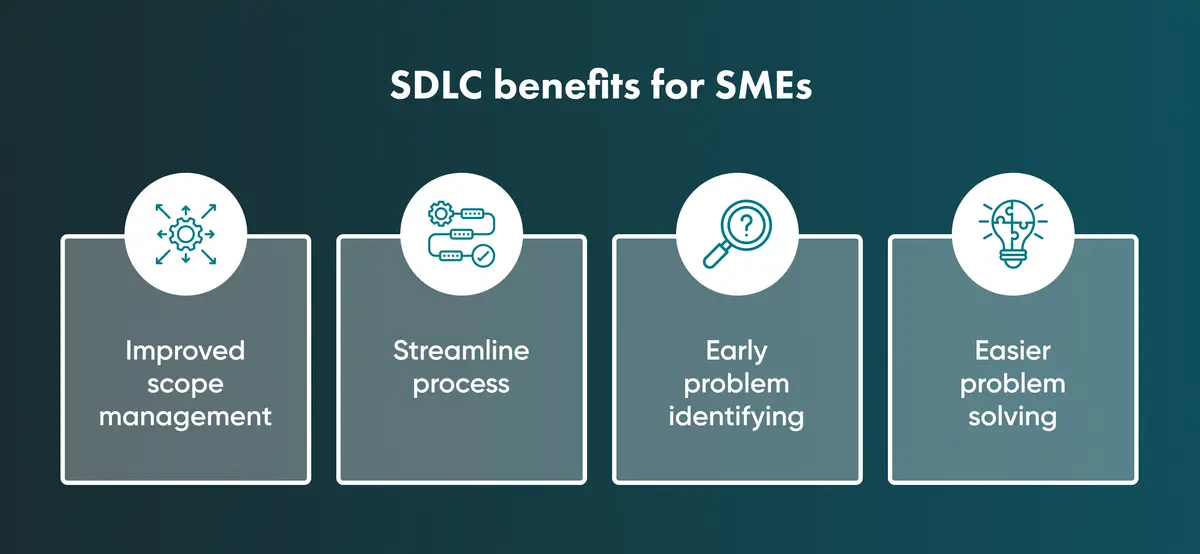
A clear SDLC pays off in three main ways.
A streamlined process
When everyone knows what stage a project is in, communication is easier and the team gets more done without extra headcount or budget.
Early problem identification
A working SDLC catches bugs early, when they are still cheap to fix, instead of letting them slip through to release.
Easier problem-solving
Sticking to one model instead of improvising keeps communication open across the team, so problems are spotted and solved faster. This applies to any project, from a booking platform for a manufacturing client to a consumer fintech product.
Talk to our engineers about where your current process is losing time.
Key takeaways
The SDLC’s basic phases have changed little since Royce drew his well-known diagram in 1970. What has changed is what “good” looks like inside it. Security now has to be designed in from the planning phase, not inspected for at the end. AI now touches almost every phase, from requirements to testing, without removing the need for a human to check the output.
Pick a model that suits your team and project, follow the 7 phases, and plan security and review of AI output from day one.
Share your project brief and we will look at where your development process can improve.
Frequently asked questions
What is the SDLC in simple terms?
The SDLC is a structured process for planning, building, testing, releasing and maintaining software. It breaks a project into defined stages, so teams always know what comes next and what “done” means at each point.
What are the 7 phases of the SDLC?
Planning, requirements and analysis, design and prototyping, development, testing, deployment, and maintenance. Different models sequence or repeat these phases differently, but most SDLCs touch all 7 in some form.
What is the difference between SDLC and Agile?
The SDLC is the overall process a project follows. Agile is one model for running that process, built around short iterations and frequent client feedback, rather than a single long, linear sequence like Waterfall.
What is a secure SDLC?
A secure SDLC builds security tasks, such as threat modelling, dependency scanning, and code review, into every phase, rather than testing for vulnerabilities only at the end. Frameworks like NIST's SSDF and regulations like the EU Cyber Resilience Act are pushing this from best practice toward a requirement.
Which SDLC model works best for a small team?
Agile or Iterative models tend to suit smaller teams best, since both allow course correction without committing months of work to a single, unchangeable plan. Waterfall works better when requirements are genuinely fixed and unlikely to shift.
How is AI changing the software development life cycle?
AI tools now assist with requirements drafting, code generation, and test case creation across most of the SDLC. Adoption is high, but so is scepticism about output quality, so most teams still treat AI as a fast first draft rather than a final answer.
Share and subscribe to our blog
Related articles

Understanding CI/CD in Software Development
What continuous integration and continuous delivery are, how they differ, the practices they rely on, and the four stages of a CI/CD pipeline.

GitOps Vs. DevOps - What are the key Differences and Challenges?
GitOps runs deployments from a Git repository; DevOps is the broader practice it belongs to. What each one is, their benefits and challenges, and how they differ.

Project Discovery Phase in Software Development
What a discovery phase is, when you need one, who takes part, what it delivers, and what happens when a software project skips it.

Kubernetes vs Docker
What deployment and containerisation are, what Docker and Kubernetes each do, how they differ and how they work together.

How can we help you ?